· ReadyStack
Worked example
Real numbers from this tool, line by line.
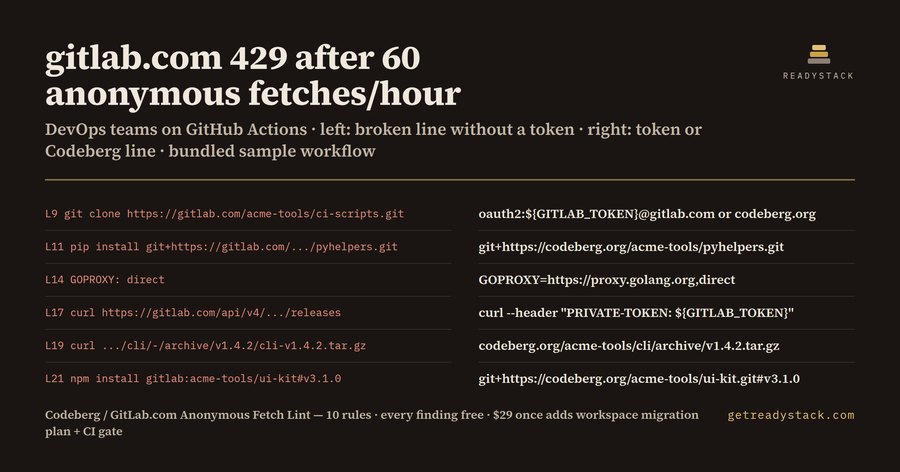
From 2026-10-19 gitlab.com answers HTTP 429 after 60 anonymous fetches per hour per IP, and for DevOps engineers running GitHub Actions in the US, the UK or the EU the sample workflow below makes 7 of them on every run.
| Line | Broken (no token) | Replacement |
|---|---|---|
| L9 | git clone https://gitlab.com/acme-tools/ci-scripts.git | https://oauth2:${GITLAB_TOKEN}@gitlab.com/... or codeberg.org |
| L11 | pip install git+https://gitlab.com/acme-tools/[email protected] | git+https://codeberg.org/acme-tools/[email protected] |
| L14 | GOPROXY: direct | GOPROXY=https://proxy.golang.org,direct |
| L17 | curl https://gitlab.com/api/v4/projects/acme-tools%2Fcli/releases | curl --header "PRIVATE-TOKEN: ${GITLAB_TOKEN}" ... |
| L19 | curl .../cli/-/archive/v1.4.2/cli-v1.4.2.tar.gz | https://codeberg.org/acme-tools/cli/archive/v1.4.2.tar.gz |
| L21 | npm install gitlab:acme-tools/ui-kit#v3.1.0 | git+https://codeberg.org/acme-tools/ui-kit.git#v3.1.0 |
| L23 | pip --index-url https://gitlab.com/api/v4/projects/41/packages/pypi/simple | a token in the index URL |
That is the output of Codeberg / GitLab.com Anonymous Fetch Lint on its bundled sample: 8 findings, 7 token-less fetches plus a warning on runs-on: ubuntu-latest.
What GitLab changed
From 2026-10-19, GitLab caps requests to gitlab.com that arrive with no credentials at 60 requests per hour per IP address; over that you get HTTP 429 with a Retry-After header (GitLab blog, 2026-09-17). Unauthenticated requests are capped no matter where they come from, including automation running against a paid account without credentials. Premium and Ultimate move in January 2027. GitLab Self-Managed and GitLab Dedicated limits stay with your operator; this is only a gitlab.com change.
The runner warning matters most. GitHub-hosted runners come from shared cloud IP ranges, so that per-IP allowance is not yours alone.
Why grep is not enough
Grep for gitlab.com also hits doc links and lines that already carry a token. The linter separates three kinds:
- anonymous fetches: git clone over https, pip git+https, npm gitlab: shorthand, curl to /api/v4, /-/archive and /-/raw downloads, .gitmodules URLs and package registry index URLs with no credentials;
- authenticated fetches it leaves alone: a token in the URL, PRIVATE-TOKEN or JOB-TOKEN headers, an insteadOf rule with a token, a .netrc entry, SSH [email protected]:;
- map entries: a go.mod path on gitlab.com is fetched through proxy.golang.org by default, so it only turns into a problem when GOPROXY=direct or GOPRIVATE covers gitlab.com.
A chatbot cannot see your files.
Two ways out per line
Every finding prints two replacement lines. The token line keeps you on gitlab.com: oauth2:${GITLAB_TOKEN}@ in the URL, a PRIVATE-TOKEN header for the API, a .netrc entry for Go. The Codeberg line is the same path on codeberg.org, with Forgejo's URL shapes: /archive/REF.tar.gz, /raw/branch/REF/PATH, /api/v1/repos/OWNER/REPO/releases and /api/packages/OWNER/ for registries.
Paying GitLab does not fix this on its own. GitLab Premium is $348 per user per year ($29 per user/month, billed annually) and does not lift the anonymous cap.
Free and key
The free part lists every anonymous fetch in the open file, with file, line and both replacement lines, from 10 rules. The licence key adds the whole-workspace migration plan, a dated exposure report and a CI gate that fails a build adding a new anonymous fetch.
15 seconds — what it actually does
Questions people ask
What does Codeberg / GitLab.com Anonymous Fetch Lint do?
It reads workflows, Dockerfiles, go.mod, requirements.txt, package.json and .gitmodules and marks every gitlab.com request sent without a token, by file and line. From 2026-10-19, GitLab caps requests to gitlab.com that arrive with no credentials at 60 requests per hour per IP address; over that you get HTTP 429 with a Retry-After header (GitLab blog, 2026-09-17). Each finding gives the replacement line: token, SSH or codeberg.org.
Who is this for?
DevOps and platform engineers whose GitHub Actions workflows, Dockerfiles or dependency manifests pull code, releases or packages from gitlab.com without signing in, and teams moving those repositories to Codeberg or Forgejo. Unauthenticated requests are capped no matter where they come from, including automation running against a paid account without credentials. GitHub-hosted runners share cloud IP ranges, so the per-IP allowance is not yours alone.
Why not just ask a chatbot or grep for gitlab.com?
A chatbot cannot see your repository, and grep for gitlab.com also hits doc links and token URLs that are fine. This linter separates the anonymous fetches from the authenticated ones, knows that go.mod paths go through proxy.golang.org unless GOPROXY=direct, and writes the replacement line for each kind: git, pip, npm, Go, API, archive, submodule, registry.
What is free and what needs a licence key?
Free, no key: every anonymous gitlab.com fetch in the open file, with file, line and the exact token or Codeberg line, from 10 rules. On the bundled sample workflow (_fixtures/dirty.yml) it reports 8 findings: 7 token-less gitlab.com fetches plus the hosted-runner warning, each with its token line and Codeberg line. A $29 licence key, once, adds the whole-workspace migration plan, a dated exposure report and a CI gate.
What does the alternative cost?
GitLab Premium is $348 per user per year ($29 per user/month, billed annually) and does not lift the anonymous cap. Unauthenticated requests are capped no matter where they come from, including automation running against a paid account without credentials. This linter finds every fetch that needs a token, SSH or a Codeberg mirror. The key is $29 once, one licence key per person or team seat.
When does the GitLab.com limit change next?
Free accounts and unauthenticated requests move to the new limits on 2026-10-19, after preview windows on October 7 and October 14 from 15:00 to 19:00 UTC. Premium and Ultimate move in January 2027. GitLab Self-Managed and GitLab Dedicated limits stay with your operator; this is only a gitlab.com change (GitLab blog, 2026-09-17).
Ask about this tool
One question, answered by the person who built it. Your email only if you want the answer sent.