· ReadyStack
Worked example
Real numbers from this tool, line by line.
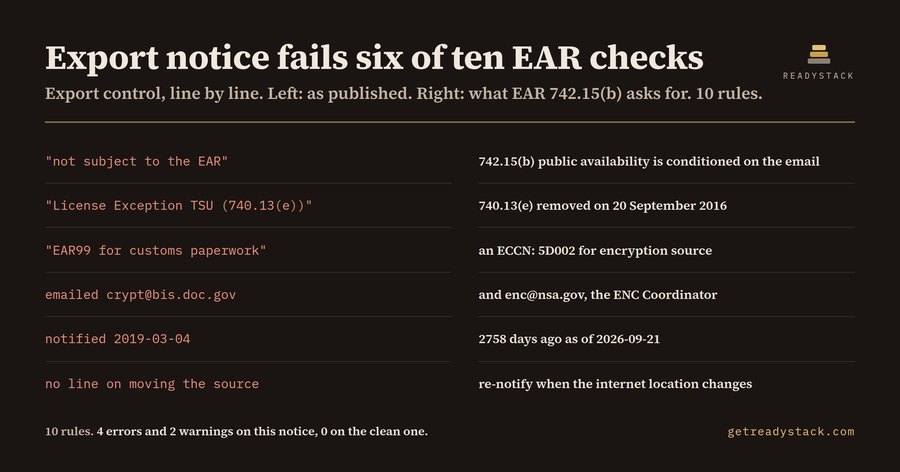
Six of ten export checks failed on one ordinary open-source notice, on a US-published secrets vault. The code was fine; the paragraph under "Export notice" was not.
That paragraph is where the US export rule actually lands. When you publish encryption source code from the United States, EAR 742.15(b) does not ask about your cipher suite. It asks whether you emailed the internet location of that source to [email protected] and to [email protected], and it asks again whenever that location changes. The public-availability position most maintainers rely on is conditioned on that email, and the notice in the repository is usually the only record that it ever went out.
Here is the notice we ran, shortened but otherwise as written:
"This project is publicly available open source, so it is not subject to the EAR and no export licence is required to download it. We publish the source under License Exception TSU (EAR 740.13(e)) and treat the package as EAR99 for customs paperwork. The notification email was sent to [email protected] on 2019-03-04."
Ten checks ran against it. Six came back, four errors and two warnings:
- "Not subject to the EAR." Public availability under 742.15(b) is conditioned on the notification. A licence file does not grant it.
- "License Exception TSU (EAR 740.13(e))." BIS removed that paragraph in the encryption rule of 20 September 2016 and moved the notification to 742.15(b). It is the most copied sentence in open-source export notices, out of date for ten years.
- "EAR99." EAR99 is not a classification for encryption source code. An ECCN such as 5D002 is.
- [email protected] with no [email protected]. The ENC Encryption Request Coordinator sits in the same sentence of the rule as BIS, and it is the address that gets dropped.
- A notification dated 2019-03-04, which is 2758 days before the day we ran the check, 2026-09-21. Everything published since then stands behind an email about a URL from seven years ago.
- No line saying a fresh notification goes out when the source moves. Repositories get renamed and mirrored, and the rule follows the location.
The clean notice shipped beside it, with both addresses, ECCN 5D002, a dated notification and a re-notify sentence, returns zero findings. The distance between the two files is about six lines of text.
Why not ask an assistant? Because the sentence an assistant hands you is sentence two above. Models reproduce the text they learned, and the pre-2016 phrasing is far more common online than the current one. More to the point, no chatbot can read the date sitting in your own notice, count 2758 days against today, and tell you which releases that email failed to cover. That is a job for something that reads your file.
Crypto Export Notice Lint is a VS Code extension and a single web page running one engine, byte for byte the same. Free and without a key: all ten checks on the notice open in the editor, marked line by line in the Problems panel, no run limit, no network call. The licensed part is a different job rather than a smaller one, on the scope and ownership axis: sweep every Markdown file in the repository and write a dated report file you keep and hand to whoever asks for it.
The yardstick is easy to name. US export-control counsel is commonly quoted at 300-600 USD per hour, and a release review is not billed in minutes.
The calendar does not stop at the email: maintainers on the mass-market encryption paths also owe an annual self-classification report by 1 February for what shipped the year before. The export paragraph is where that trail starts.
15 seconds — what it actually does
Questions people ask
What does this actually do?
It reads the export-control paragraph in your Markdown — README, EXPORT, NOTICE, SECURITY — and reports which of ten documented items are absent or wrong: the [email protected] and [email protected] addresses, the published source URL, an ECCN such as 5D002, the notification date, the removed 740.13(e) citation, and the line about re-notifying when the source moves.
Who is it for?
Maintainers and founders who publish source code containing encryption from the United States: the person who tags a release of a password manager, an end-to-end messaging client, a database with encryption at rest, or an SDK that wraps libsodium or OpenSSL. Also the security engineer who inherits that repository and its export paragraph.
Why will a free chatbot not do this?
Because the paragraph most assistants reproduce cites License Exception TSU at EAR 740.13(e), which BIS removed in the encryption rule of 20 September 2016 and replaced with the notification in 742.15(b). A generative answer restates the text it learned; it cannot tell you that your own notice is dated 2019 and missing [email protected].
What is free and what needs a key?
Checking the file open in your editor against all ten checks is free forever, with no key, no watermark and no run limit. The licence key covers a different axis: sweeping every Markdown file in the repository and writing a dated report file you own.
What did it find on the sample notice?
Six findings on one ordinary-looking export paragraph — four errors and two warnings: no [email protected], no ECCN, a removed 740.13(e) citation, an EAR99 claim, a notification dated 2019-03-04 and no re-notify line. The clean notice shipped beside it returns zero. US export-control counsel is commonly quoted at 300-600 USD per hour.
Why not just ask ChatGPT or another AI chat?
A general AI chat answers from training data with a cutoff date, cannot read your repository and names no rule version. Crypto Export Notice Lint (EAR 742.15) checks the file you open against 10 rules from a rule set dated 2026-09-21, and points at the exact line. For a filing, an audit or a client you need that dated result on your own files.
Ask about this tool
One question, answered by the person who built it. Your email only if you want the answer sent.