· ReadyStack
Worked example
Real numbers from this tool, line by line.
Twenty-four findings in forty-five lines. That is what the fixture shipped with PII-in-Logs Lint returns for one Express signup route — the kind a Node engineer in Berlin or Dublin inherits in their first week — and fifteen of those twenty-four are errors, not style warnings.
The file is not badly written. It is written the way a coding assistant writes it. Ask one to "add logging to this handler" and it logs the object it has, because the object it has is the request:
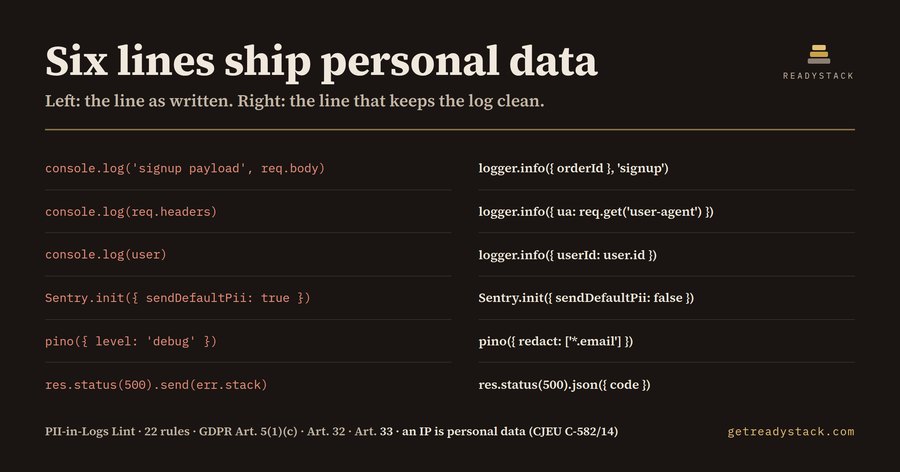
console.log('signup payload', req.body);That line compiles, passes review, and runs for years. It copies every signup body — name, email, date of birth, sometimes a card — into stdout, into the log shipper, into the vendor's index, and into backups that outlive the service.
The clock is 72 hours, and it starts when someone notices
Art. 5(1)(c) says collect the minimum, Art. 32 says secure what you hold, and Art. 33 gives you seventy-two hours to notify a supervisory authority once you become aware of a personal-data breach. The clock starts the day someone opens the log viewer and sees a customer's address — which is how a line written in 2023 becomes a deadline in 2026. The next wave of US state privacy laws lands on 1 January 2027.
The findings that do not look like personal data
Some of the twenty-four never mention a person. morgan('combined') writes the client IP on every request, and an IP address is personal data in the EU — CJEU C-582/14, *Breyer*. sendDefaultPii: true tells the Sentry SDK to attach the IP, cookies, headers and request body to every event.
Another group lives in the bootstrap file: pino({ level: 'debug' }) with no redact, a winston file transport with no maxFiles — Art. 5(1)(e) storage limitation has no "forever" setting — a DEBUG=*, and an ORM started with log: ['query']. None of them appear in a diff that only touched a route handler.
The same route, written the other way
The second fixture is the same service: same route, same framework, same error handling. It logs { orderId } instead of req.body, initialises pino with a redact list, sets sendDefaultPii: false, gives the file transport a maxFiles, and returns an error code instead of a stack. It scores 0 findings against all 22 rules. None of those fixes are hard. They are just invisible until something counts them.
Why the tools you already have miss it
ESLint's no-console treats every console call identically, which is why teams switch it off — it cannot tell req.body.orderId from req.body. Secret scanners look for keys and tokens; a customer's name is neither. A chatbot will explain Art. 33 to you but cannot see that line 30 of routes/signup.js is the problem. The gap is not knowledge. It is location.
What the extension does
Twenty-two rules, plain regular expressions you can read in ext/rules.json before you trust them: request objects, person records and fields, credentials and sessions, logger configuration, third-party sinks, outward leaks, source hygiene. Each finding gives the line, the rule, the article and the fix.
The file you have open is free — all 22 rules, no key, no limit. The paid tier, $29 once, runs the same rules across every .js and .ts file in the workspace and writes the findings to a report file you keep. One licence key per person or CI seat. GitHub Advanced Security lists at $49 per active committer per month and hunts secrets rather than people.
Run the same 22 rules free, in the browser, on one file: https://getreadystack.com/tools/log-pii-telemetry-lint
15 seconds — what it actually does
Questions people ask
What does PII-in-Logs Lint actually do?
It reads a JavaScript or TypeScript file and marks each line that sends personal data to a log sink: console.log(req.body), a whole user record, a password or token argument, sendDefaultPii: true, morgan('combined') writing the client IP, pino with no redact option, or a stack trace returned to the caller. Each finding names the rule and the fix.
Who is it for?
Node and TypeScript backend engineers whose service handles EU personal data, and the platform engineer who has to say which services log what. It is written for the person who inherited a repo where logging was added by a coding assistant and nobody has read every console call since.
Why is ESLint or a secret scanner not enough?
ESLint's no-console rule treats every console call the same way, so teams switch it off; it cannot tell req.body.orderId from req.body. Secret scanners hunt keys and tokens, which are not personal data. Neither one knows that an IP address is personal data in the EU under CJEU C-582/14.
What is free and what costs money?
The file you have open is free, with all 22 rules, no key and no limit — you can clean a file with it and never buy anything. The paid tier, $29 once, runs the same rules across every .js and .ts file in the workspace and writes the findings to a report file you keep. Scope and ownership, not crippled rules.
What would this cost otherwise?
GitHub Advanced Security lists at $49 per active committer per month, split as $30 Code Security and $19 Secret Protection, and it looks for secrets rather than for personal data in log lines. A privacy engineer reading one service's logging calls by hand is a day of work per service, repeated each release.
Why not just ask ChatGPT or another AI chat?
A general AI chat answers from training data with a cutoff date, cannot read your repository and names no rule version. PII-in-Logs Lint (console.log(req.body)) checks the file you open against 22 rules from a rule set dated 2026-09-20, and points at the exact line. For a filing, an audit or a client you need that dated result on your own files.
Ask about this tool
One question, answered by the person who built it. Your email only if you want the answer sent.