Check your OWASP Dependency Check setup in pom.xml, Gradle, suppression XML and CI files for plugin versions below the mandatory upgrade, expired suppressions, hardcoded…

Try it freeFull version · $29 once →
What you get: Scans every build, suppression and CI file in the workspace at once, exports a dated audit report and runs the same check in CI with a team key.
Updated 2026-10-01 · ReadyStack
OWASP dependency check setup lint for pom.xml, Gradle, suppression XML and CI files: plugin versions below the 12.1.0 mandatory upgrade, expired suppressions, hardcoded NVD API keys, failBuildOnCVSS 11. Runs entirely in your browser — nothing is uploaded.
Same engine as the VS Code extension, byte for byte.
Free for the file open in your editor - no key, no limit. The workspace sweep and the report ask for a key.
VS Code MarketplaceOpen VSX (Cursor, VSCodium)ext install ReadyStack.owasp-dependency-check-config-lint
Team? One key for every ReadyStack linter, 5 seats, $149 once
Scans every build, suppression and CI file in the workspace at once, exports a dated audit report and runs the same check in CI with a team key.
One payment, one licence key for this tool. The key is shown right after payment.
Snyk Team starts at $25 a month (snyk.io/plans, checked 2026-10-01); this lint is $29 once and keeps the free scanner you already run.
Buy the full version — $29Need more than this one? ReadyStack Pass opens all 679 files and 561 full versions — $29/month or $199/year. See the Pass →
· ReadyStack
Real numbers from this tool, line by line.
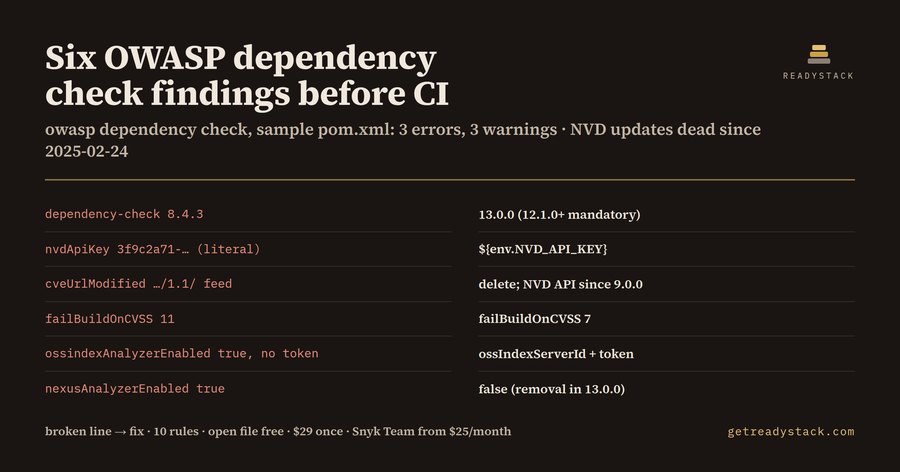
OWASP dependency check: six setup findings in a sample pom.xml, and the dates behind them
Six findings — three errors and three warnings — came back when OWASP Dependency Check Config Lint read the sample pom.xml of a Java billing API, the Maven build a team lead in a US or EU payments shop inherits. None of them is a CVE. All of them decide whether the CVE scan still works.
OWASP Dependency-Check is free and widely used in Maven and Gradle builds. Its configuration has broken on fixed dates, and the README on GitHub lists them:
The sample pom.xml pins dependency-check-maven through a property, dependency-check.version, set to 8.4.3. The lint resolves the property and reports on the version line.
| Broken line | Fix |
|---|---|
| dependency-check 8.4.3 | 13.0.0 (12.1.0+ mandatory) |
| nvdApiKey 3f9c2a71-... (literal) | ${env.NVD_API_KEY} |
| cveUrlModified .../1.1/ feed | delete; NVD API since 9.0.0 |
| failBuildOnCVSS 11 | failBuildOnCVSS 7 |
| ossindexAnalyzerEnabled true, no token | ossIndexServerId + token |
| nexusAnalyzerEnabled true | false (removal in 13.0.0) |
failBuildOnCVSS 11 is the default, and since CVSS stops at 10.0 the build can never fail on a CVE. The OSS Index line looks switched on, but with no token the analyzer is turned off for you.
A suppression file can carry an until date:
<suppress until="2026-09-15Z">
<cve>CVE-2020-36518</cve>
</suppress>
On that day the suppression stops applying and the CVE is reported again. The lint compares every until with today: past dates are errors, dates within 30 days are warnings. Run on 2026-10-01, the sample suppression file gives one error (2026-09-15) and one warning (2026-10-20). Run on 2026-11-01, both are errors.
Ask a chatbot for a dependency-check-maven block and you often get an older version number and the cveUrlModified setting, because most examples online predate 9.0.0. The docs do not point at your line.
ODC001 version below 12.1.0 · ODC002 legacy NVD feed setting · ODC003 hardcoded NVD API key or OSS Index password · ODC004 no NVD API key · ODC005 failBuildOnCVSS above 10 · ODC006 suppression until date · ODC007 OSS Index on without a token · ODC008 legacy OSS Index credentials · ODC009 Java 8 runtime · ODC010 Nexus v2 analyzer.
Linting the open file is free, with every finding and fix line. The full version scans every build, suppression and CI file in the workspace, exports a dated audit report and runs the same check in CI with a team key. For comparison, Snyk Team starts at $25 a month on its plans page, checked 2026-10-01, and replaces the scanner instead of checking it.
It reads the files that run OWASP dependency check — pom.xml, build.gradle, dependency-check-suppression.xml and CI workflow YAML — and flags setup breaks on their exact line: plugin versions below the 12.1.0 mandatory upgrade, retired NVD feed settings, hardcoded NVD API keys, failBuildOnCVSS 11, expired suppression until dates, OSS Index without a token, Java 8 runners and Nexus v2. Each finding carries the replacement line and a dated source.
Java and JVM team leads, build engineers and AppSec owners who run OWASP dependency check in Maven, Gradle or a CI pipeline, and anyone who inherited a pom.xml with a dependency-check-maven block nobody has touched since 2023. It also fits auditors who must show the scan was current and able to fail the build on a given date.
The breaking points are dated: 9.0.0 moved to the NVD API on 2023-11-22, 11.0.0 needs Java 11, issue #7463 made 12.1.0 mandatory on 2025-02-24, and OSS Index tokens became required in September 2025. A chatbot often answers from older docs, and reading the docs does not tell you which line in your own pom.xml is affected. This lint checks each line against those dates.
Free: lint the open file and see every finding with its fix line, with no key and no limit. The full version, $29 once, scans every build, suppression and CI file in the workspace at once, exports a dated audit report, and runs the same check in CI with a team key, so a clean result can be shown to an auditor.
Snyk Team starts at $25 a month per the snyk.io plans page checked on 2026-10-01, and it replaces your scanner rather than checking it. This lint costs $29 once and keeps the free OWASP Dependency-Check scanner you already run. It only checks that the scan can still update its NVD data, keeps its suppressions current and can fail the build.
One question, answered by the person who built it. Your email only if you want the answer sent.
Paste this code into your page. It runs in your visitor’s browser and stays up to date. Nothing your visitors type is stored.
For businesses: your name and logo instead of ours, and each visitor’s result + e-mail in your inbox (only when they tick consent) — Pro from $19/month. See Pro →
For a team or company: for an invoice with your company details, a quote or several licences, write to [email protected].
Neo4j End of Life — map dependencies and end of lifeThis tool finds Neo4j images, licence lines, drivers, and Bolt URIs in project files and dates them against Neo4j end of life.FreeFull version $29
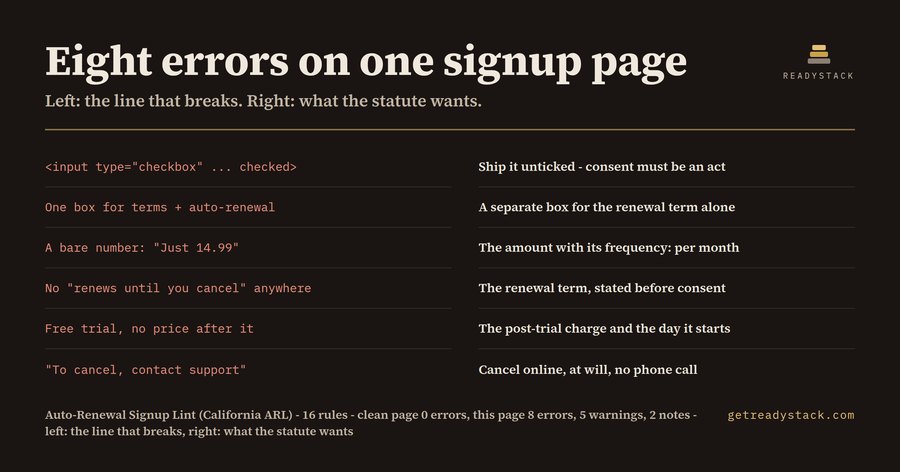
California Auto Renewal Law 2026 — check signup pages under californiaChecks subscription signup and pricing pages against California’s Automatic Renewal Law as amended by AB 2863, in force from January 1…FreeFull version $29
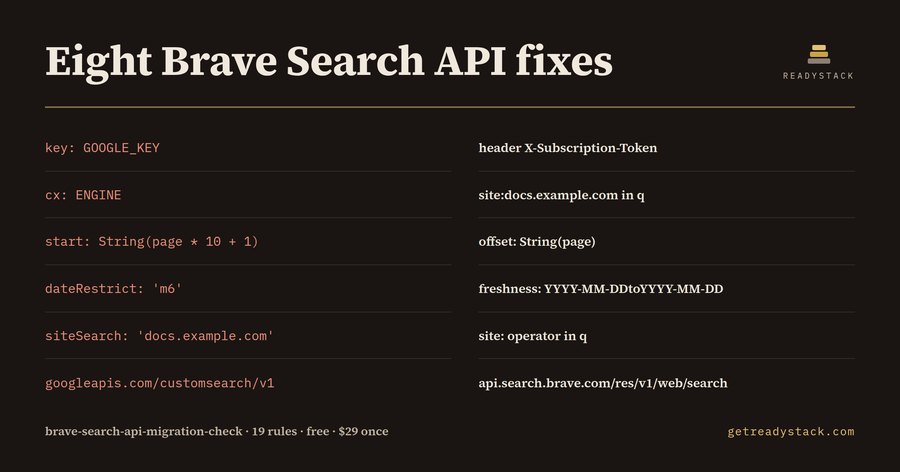
Bing Search API retired — check your code for freeCheck code for retired Bing v7 calls and Google Custom Search JSON API calls, with a Brave Search API rewrite for each flagged line.FreeFull version $29
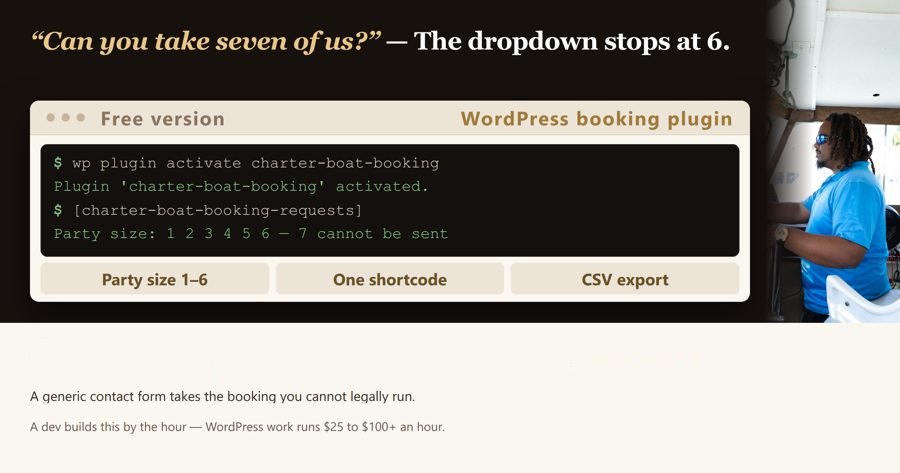
Charter Boat Booking Requests — 6-Passenger LimitTrip requests for six-pack charter boats: the party-size list stops at 6, so a trip your OUPV license cannot carry never reaches your inbox.FreeFull version $6
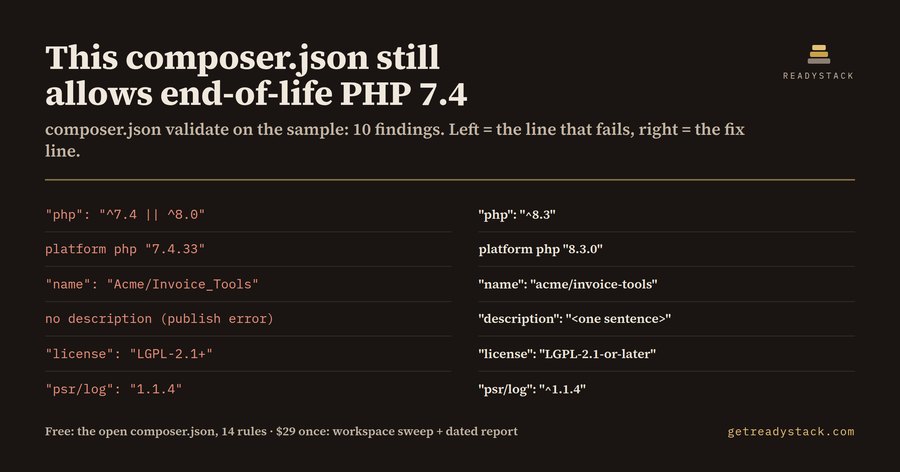
PHP 8.1 end of life — check php requirements before releaseThis free browser tool checks composer.json PHP version requirements and fields rejected by strict validation.FreeFull version $29Consent Mode v2 Lint for GA4 & Google AdsFinds the consent-signal bugs that silently switch off Google Ads conversions and remarketing for EEA and UK traffic - in your source…FreeFull version $29ReadyStack
Calculators, templates and deadlines for the rules that change every year — free in your browser.