· ReadyStack
Worked example
Real numbers from this tool, line by line.
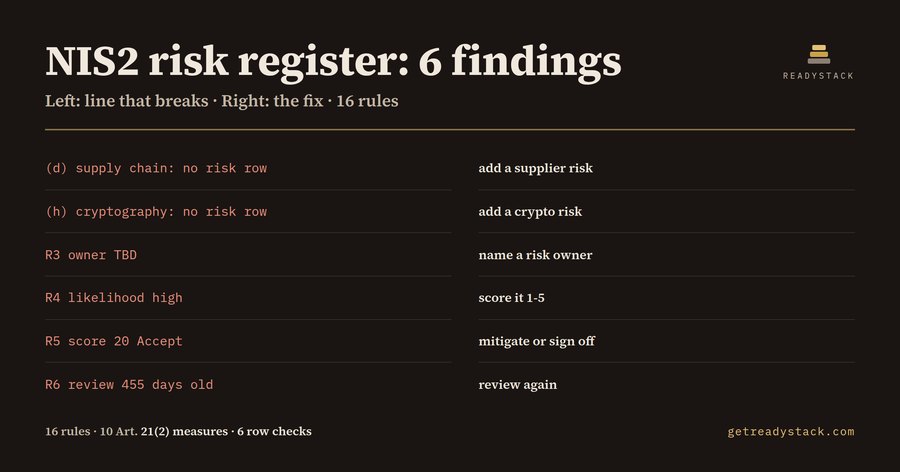
6 findings in one NIS2 risk register: that is what Risk Register Lint returned for the sample register of an EU grid operator, the kind of Markdown table a CISO or security lead at an essential or important entity keeps in Git and hands to an auditor.
The six findings, measured on 2026-09-28:
- 2 missing measures: no risk row cites Art. 21(2)(d) supply chain security or Art. 21(2)(h) cryptography and encryption.
- 1 risk owner written as "TBD" (row R3).
- 1 likelihood written as "high" instead of a 1-5 score (row R4).
- 1 risk scored 4x5 = 20 and marked Accept with no mitigation (row R5).
- 1 review dated 2025-06-30, which is 455 days old against a 365-day cycle (row R6).
The clean sample register, ten rows that cite all ten letters, returns 0 findings.
Why the register is the document that gets read
NIS2, Directive (EU) 2022/2555, Article 21(2) lists ten risk-management measures: (a) risk analysis and information system security policies, (b) incident handling, (c) business continuity and crisis management, (d) supply chain security, (e) security in acquisition, development and maintenance including vulnerability handling, (f) assessing the effectiveness of the measures, (g) cyber hygiene and training, (h) cryptography and encryption, (i) human resources security, access control and asset management, (j) multi-factor authentication and secured communications.
Article 20 makes the management body approve these measures. Article 34 lets authorities fine essential entities up to at least EUR 10,000,000 or 2 % of worldwide annual turnover, and important entities up to at least EUR 7,000,000 or 1.4 %. When a supervisor asks how you manage supply chain risk and the register has no row for it, the gap is on paper.
What a chatbot does not do
Paste the register into a chatbot and it will tidy the table. It will not reliably count which of the ten letters are present, and it does not compare your review column with today's date. A Markdown linter checks pipes and alignment, not content.
How the check works
Risk Register Lint finds any Markdown table whose header has an Owner and a Treatment column, then locates the other columns by name: ID, Art. 21(2), Likelihood, Impact, Last review. It runs 16 rules:
- 10 coverage rules, one per letter (a) to (j). A letter nobody cites becomes one finding on the header line.
- 6 row rules: owner missing (empty, TBD, n/a), likelihood or impact not 1-5, treatment not mitigate/accept/transfer/avoid, review date missing or in the future, review older than 365 days, and a score of 15 or more marked Accept.
The row rules follow ISO/IEC 27001: risk owners (6.1.2), likelihood and consequences (6.1.2), treatment options and owner approval of residual risk (6.1.3), and assessment at planned intervals (8.2).
The date matters. Run the clean register as of 2026-12-01 instead of 2026-09-28 and row R4, last reviewed 2025-11-04, turns stale at 392 days: 1 finding where there were 0.
Free and full version
The free version checks one register completely, all 16 rules, with line numbers, in VS Code or in the browser page, which runs the same engine. Nothing is uploaded. The full version scans every register in a workspace in one pass and exports a dated audit evidence file that maps each finding to its Art. 21(2) letter.
It checks structure and coverage, not whether a control is adequate. That judgement stays with you and your auditor.
15 seconds — what it actually does
Questions people ask
What does Risk Register Lint do?
It reads a Markdown risk register and runs 16 rules: ten check that every NIS2 Article 21(2) measure (a) to (j) is cited by at least one risk row, and six check each row for a named owner, a 1-5 likelihood and impact, a valid treatment, a real review date and a review inside 365 days. Each finding carries a line number.
Who is it for?
It is for CISOs, security leads and compliance engineers at EU essential and important entities under NIS2, such as energy, water, transport, health and digital infrastructure operators, who keep their cybersecurity risk register as a Markdown table in a Git repository and want it audit-ready before a supervisor or certification auditor reads it.
Why not just ask a chatbot or use a free Markdown linter?
A Markdown linter checks table syntax, not content. A chatbot can rewrite the table but does not reliably count which of the ten Art. 21(2) letters are cited and does not compare your review column with today's date. Risk Register Lint does both deterministically: the sample register gives the same 6 findings on every run.
What is free and what needs a licence key?
Free: one register, all 16 rules, with line numbers, in VS Code or the browser page. On the sample register it finds 6 findings: 2 missing measures (d) and (h), 1 owner TBD, 1 likelihood written as high, 1 score 20 risk accepted, 1 review 455 days old. The licence key adds a workspace-wide scan and a dated audit evidence export.
What does getting it wrong cost?
NIS2 Article 34 lets authorities fine essential entities up to at least EUR 10,000,000 or 2 percent of worldwide annual turnover, and important entities up to at least EUR 7,000,000 or 1.4 percent. Article 20 makes the management body approve the Article 21 measures, so a gap in the risk register reaches the board, not only the security team.
Why not just ask ChatGPT or another AI chat?
A general AI chat answers from training data with a cutoff date, cannot read your repository and names no rule version. Risk Register Lint — NIS2 Art. 21(2) checks the file you open against 16 rules, each naming its legal or official basis, from a rule set dated 2026-09-28, and points at the exact line. For a filing, an audit or a client you need that dated result on your own files.
Ask about this tool
One question, answered by the person who built it. Your email only if you want the answer sent.