· ReadyStack
Worked example
Real numbers from this tool, line by line.
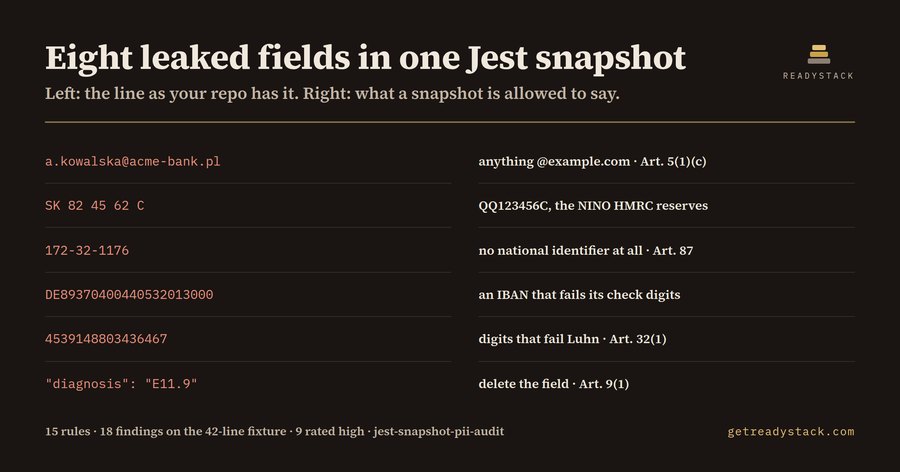
Eight leaked fields came out of one 42-line Jest snapshot file: an IBAN that passes its ISO 13616 check digits, a payment card that passes Luhn, a diagnosis code, a UK National Insurance number, a live session cookie, a bearer token, a public IP and a date of birth sitting next to a surname. The team that committed it was an ordinary JavaScript shop shipping a billing screen to EU customers. Nobody there had decided to store any of it.
Snapshot testing is what put it there. You call toMatchSnapshot(), Jest writes down whatever the component rendered, and the file lands in __snapshots__ next to the test. If the fixture behind the render came from staging, or from a recorded production response that an assistant pasted in while writing the test for you, the snapshot keeps the entire payload. Then it goes into git, and git keeps it for as long as the repository exists — in every clone, on every laptop, in the CI cache.
The uncomfortable part is which tool is supposed to catch this. Secret scanners match credential shapes: a private key block, an AWS access key id, a token prefix. They are good at that, and they do flag the bearer token in the example above. What they will never flag is:
"firstName": "Anna", "lastName": "Kowalska", "dateOfBirth": "1979-04-02", "postalCode": "1049",
because none of it looks like a secret. Under GDPR Art. 4(1) that block is personal data, full stop, and a repository is not a place you have a lawful basis to keep it. If it leaves — a fork, a contractor, a public mirror — Art. 33 gives you 72 hours from becoming aware to notify your supervisory authority, and that notification has to say which categories of data were involved.
Jest Snapshot PII Audit is a VS Code extension that reads .snap files line by line under 15 rules and names the article each line touches. Five rules are arithmetic rather than pattern matching, which is the difference between a usable tool and a wall of noise. iban_valid takes the account number mod 97, so an invented IBAN is silent. payment_card runs Luhn and demands a real issuer prefix. public_ip drops loopback, RFC 1918, carrier-grade NAT, link-local and the RFC 5737 documentation ranges — the Court of Justice treated a dynamic IP held by an operator as personal data in C-582/14, Breyer. person_name and postal_address compare the value against a placeholder vocabulary: Jane, Doe, foo, [redacted], all-zero postcodes, and stay quiet when the fixture was obviously invented.
The numbers above are measured, not estimated. The fixture that ships inside the package, _fixtures/dirty.snap, is 42 lines and returns 18 findings, 9 of them rated high, covering all 15 rules. Its twin, _fixtures/clean.snap, renders the same component with placeholder values and returns 0. A third sample — an 18-line recording of a German checkout API, with vorname, nachname, strasse and plz instead of English field names — returns 8 findings, 3 high, across 6 rules. Different input, genuinely different answer.
Scanning the file you have open is free and needs no key, and that finishes that file. The licensed version does a different job: one pass across every .snap in the repository, written out as a dated evidence file for a DPO or an auditor. For scale, a freelance privacy consultant reading one repository by hand bills $80-150 an hour.
The same engine.js and rules.json run as a web page with nothing uploaded, so you can paste a snapshot and see all 15 rules before installing anything.
15 seconds — what it actually does
Questions people ask
What does Jest Snapshot PII Audit actually do?
It reads your Jest .snap snapshot files line by line and names every line that carries real personal data or a live credential: e-mail addresses, national identification numbers, IBANs that pass their check digits, card numbers that pass Luhn, JWTs, session cookies, public IP addresses, dates of birth and special category fields. Each hit carries the GDPR article it touches and what to write instead.
Who is this for?
JavaScript and TypeScript developers on EU and UK product teams, especially ones whose snapshots were recorded from a staging or production API. It is aimed at people who write toMatchSnapshot against a real HTTP response, and at the reviewer who has to sign off that the repository holds no customer data before an audit.
Why will a normal secret scanner not catch this?
Secret scanners match credential shapes: an AWS key, a GitHub token, a private key block. They do not flag Anna Kowalska sitting next to a birth date and a postcode, because none of that looks like a secret. Under GDPR that combination is exactly what counts as personal data, and it is the part that a breach notification has to describe.
What is free and what does the paid version add?
Free scans the .snap file you have open and reports every finding with its rule, article and line number, so you can clean that file completely and never pay. The paid licence adds a different job: it sweeps every .snap in the repository in one pass and writes the run out as a dated evidence file you can hand to your DPO or auditor.
What would it cost to have a person do this?
A freelance privacy consultant reading one repository by hand bills $80-150 an hour on EU marketplaces, and a repository with a few hundred snapshot files is not a one-hour job. Counting your own developer hours, a manual pass over the snapshots before an audit usually costs more than the licence does, and it has to be repeated after every recorded response.
Does anything leave my machine?
No. The rules and the matching run locally inside the extension, and the free web page runs the same JavaScript in your browser tab. Snapshot contents are never uploaded. Only the licence key check contacts a server, and it sends the key and an organisation id, nothing from your code.
Why not just ask ChatGPT or another AI chat?
A general AI chat answers from training data with a cutoff date, cannot read your repository and names no rule version. Jest Snapshot Lint - PII and secrets in __snapshots__ checks the file you open against 15 rules, each naming its legal or official basis, from a rule set dated 2026-09-20, and points at the exact line. For a filing, an audit or a client you need that dated result on your own files.
Ask about this tool
One question, answered by the person who built it. Your email only if you want the answer sent.