· ReadyStack
Worked example
Real numbers from this tool, line by line.
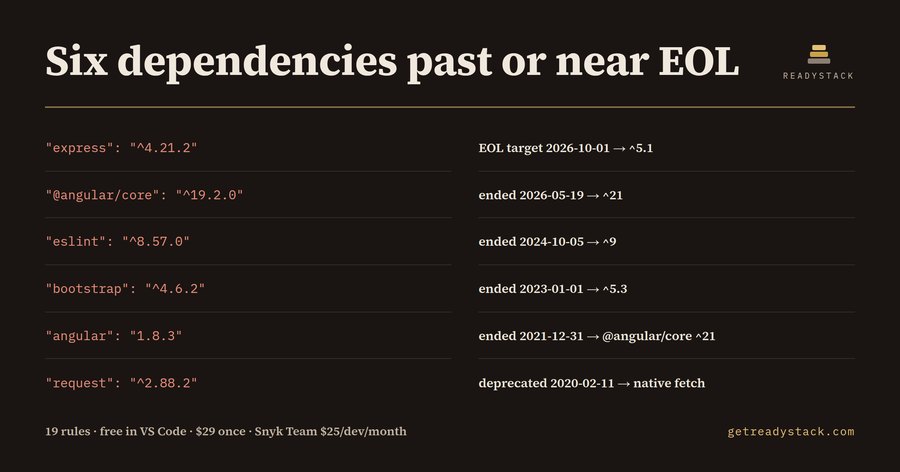
Dependency checker result: six dependencies in a sample Angular and Express package.json are past or near end of support. Five are already past their published end date, and Express 4 reaches its end-of-support target on 2026-10-01. If you are an agency or freelance web developer maintaining client apps in the US, the UK or the EU, this is the list your client's security reviewer will ask for.
The file
The sample is an ordinary Angular 19 app with an Express API and an AngularJS module still running through ngUpgrade. It builds, it deploys and every test passes. Here is what the dependency checker printed on 2026-09-28:
| Pinned line | Support end and fix |
|---|---|
| "express": "^4.21.2" | EOL target 2026-10-01 (no sooner than) → ^5.1 |
| "@angular/core": "^19.2.0" | ended 2026-05-19 → ^21 |
| "eslint": "^8.57.0" | ended 2024-10-05 → ^9 |
| "bootstrap": "^4.6.2" | ended 2023-01-01 → ^5.3 |
| "angular": "1.8.3" | ended 2021-12-31 → @angular/core ^21 |
| "request": "^2.88.2" | deprecated 2020-02-11 → native fetch |
Five errors, one warning. The upgraded version of the same file returns zero findings.
Why npm outdated did not catch it
npm outdated compares your pin with the newest release. It will tell you that 21 is newer than 19. It will not tell you that 19 stopped getting security patches on 2026-05-19, or that Express marks 2026-10-01 as the earliest end of life for version 4. pip list --outdated and composer outdated work the same way. Nothing breaks on the end date, so nothing in your pipeline goes red.
The dates live on a different page for every project: angular.dev, expressjs.com/en/support, eslint.org/version-support, djangoproject.com, laravel.com/docs/releases. Code assistants make it worse in one specific way: they suggest the majors they saw most in training, so a project scaffolded this year can start on a line that is already out of support.
What the checker does
The extension stores 19 rules. Each one is a package, a version range, an end date and the page the date came from:
- npm: AngularJS 1.x, Angular 16 and older, 17, 18, 19 and 20, Vue 2, Nuxt 2, Bootstrap 4 and older, Express 4, ESLint 8 and older, request, react-scripts
- pip: Django 3.2 and older, Django 4.x, Django 5.0 and 5.1
- Composer: Laravel 9 and older, Laravel 10, Laravel 11
It reads the first version number of each range, compares it with today's date and reports past dates as errors and dates within 120 days as warnings. Change the date and the answer changes: the same package.json checked on 2026-05-01 shows Express 4 as clear and Angular 19 as a warning, because the end dates are now 153 and 18 days away.
WARN L16 express-4-eol  Express 4 (express ^4.21.2) reaches end of support on 2026-10-01 (target, no sooner than)
ERRO L12 angular-19-eol Angular 19 (@angular/core ^19.2.0) is past end of support since 2026-05-19
Free and full
The free extension and the free web page check the manifest you open and show every finding, every date and every upgrade target. Nothing is uploaded. The full version scans every package.json, composer.json and requirements file in a workspace in one run and exports a single dated report as CSV and Markdown, the file you hand to a client or an auditor. For comparison, Snyk Team is listed at $25 per contributing developer per month; it focuses on known vulnerabilities rather than end-of-support dates.
Open your own package.json before 2026-10-01 and look for the Express line first.
15 seconds — what it actually does
Questions people ask
What does the Dependency Checker — EOL Dates extension do?
It reads package.json, composer.json and requirements.txt, takes the version you pinned for Angular, AngularJS, Vue, Nuxt, Bootstrap, Express, ESLint, request, react-scripts, Django and Laravel, and compares it with 19 published end-of-support dates. Past dates become errors, dates within 120 days become warnings, and each finding names the date, its source and the version to upgrade to.
Who is this dependency checker for?
Agency and freelance web developers who maintain client apps built on Angular, Express, Django or Laravel, and the tech leads who must answer 'is anything we ship out of support?' before a security review, a renewal or a handover. It also suits anyone reviewing a project an AI assistant scaffolded, because generated manifests often pin older majors.
Why not just use npm outdated or Dependabot?
npm outdated, pip list --outdated and composer outdated compare your pin with the newest release; they never print the date your current major stops receiving security fixes. Angular 19 still builds after its 2026-05-19 end date, so nothing fails. This extension stores each end date and source, so the finding says exactly when support ended or will end.
What is free and what does the full version add?
Free, with no key: checking the open manifest in VS Code or on the web page, with every finding, date and upgrade target shown. The full version, $29 once with one licence key per person or team seat, scans every manifest in the workspace in one run and exports a single dated EOL report as CSV and Markdown for a client or an audit.
What does the alternative cost?
Snyk Team is listed at $25 per contributing developer per month, which is $300 a year for each developer; it focuses on known vulnerabilities rather than end-of-support dates. Checking by hand means opening angular.dev, expressjs.com, eslint.org, djangoproject.com and laravel.com for every project. The full version of this extension is a one-time $29 licence.
Why not just ask ChatGPT or another AI chat?
A general AI chat answers from training data with a cutoff date, cannot read your repository and names no rule version. Dependency Checker — EOL Dates checks the file you open against 19 rules from a rule set dated 2026-09-28, and points at the exact line with the fix. For a filing, an audit or a client you need that dated result on your own files.
Ask about this tool
One question, answered by the person who built it. Your email only if you want the answer sent.