Claude Code skills · updated 2026-10-03
TLS cert validity skill for Claude Code — 200/100/47-day caps, openssl -days
Flags cert scripts, Terraform and cert-manager values that break under SC-081v3
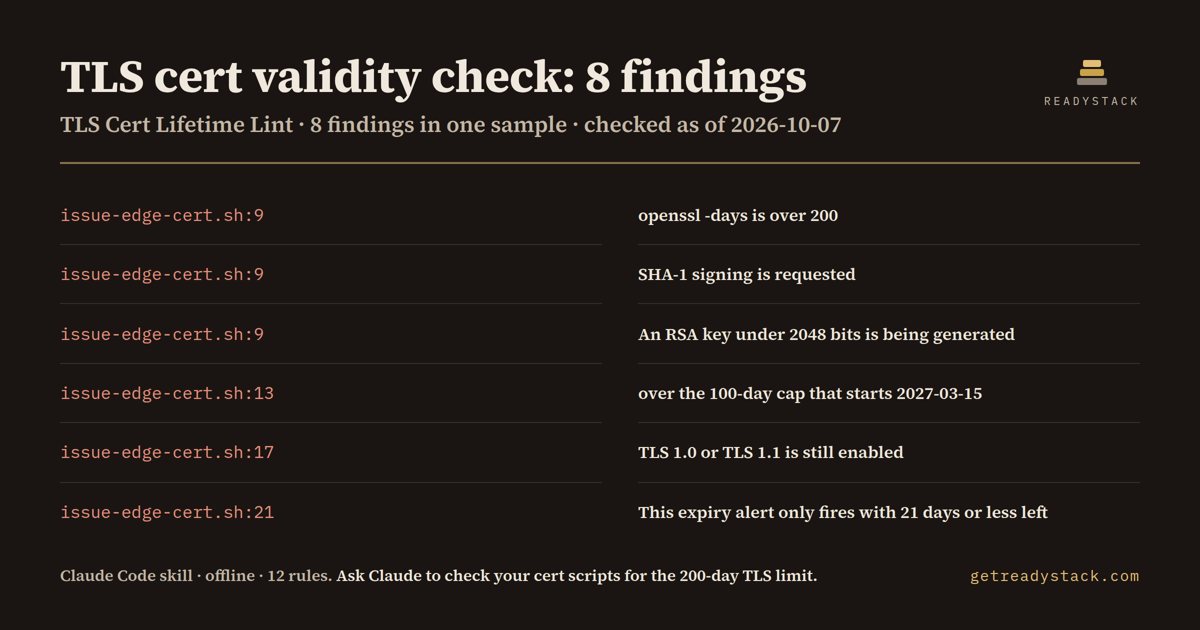
On one 22-line shell script it printed 8 findings (5 errors, 3 warnings) from 12 rules, each with file:line, what breaks, the date and the fix.
Get it on Whop - $12 onceGet it on Gumroad
Who it's for
For DevOps and platform engineers who issue TLS certificates from shell scripts, Terraform or cert-manager and own the renewal pipeline.
What breaks, and when
Since 2026-03-15 a public TLS certificate may not exceed 200 days, and on 2027-03-15 the cap falls to 100 days (SC-081v3): openssl -days 365 is refused or truncated.
What it printed on the bundled example
== TLS Cert Lifetime Lint — 8 findings (5 errors, 3 warnings) in 1 file · 12 rules
  WARN  issue-edge-cert.sh:8  [stale-max-lifetime-claim]
        This text still states the old 397, 398 or 825-day maximum. The public TLS maximum has been 200 days since 2026-03-15, becomes 100 days on 2027-03-15 and 47 days on 2029-03-15 (SC-081v3), so anyone planning a renewal from this line plans it wrong.
        fix: State the current cap and the two dated step-downs.
  ERROR issue-edge-cert.sh:9  [openssl-days-over-200]
        openssl -days is over 200. Since 2026-03-15 a publicly trusted TLS certificate may not exceed 200 days (CA/Browser Forum ballot SC-081v3), and the cap falls to 100 days on 2027-03-15. A public CA will refuse or truncate this request.
        fix: Use -days 90 and let ACME renew, or keep this key for an internal CA only.
  ERROR issue-edge-cert.sh:9  [sha1-signature]
        SHA-1 signing is requested. Public CAs stopped signing SHA-1 certificates in 2016 and browsers reject the chain outright, so this certificate cannot be used on a public endpoint.
What you get
- A scanner Claude runs over every .sh, .tf, .yaml, .conf, .go and .md file - not a summary from memory
- 12 rules dated to SC-081v3: 200 days now, 100 on 2027-03-15, 47 on 2029-03-15
- Each finding: file:line, what breaks, the date and the replacement line
- Claude applies edits only after you say yes; exit 1 in CI
Install
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "Can you check whether our certificate scripts and cert-manager config will break with the new shorter TLS certificate validity periods? Don't edit anything yet.". Needs Node 16+.
unzip tls-cert-validity-check.zip -d ~/.claude/skills/
Ask Claude
“Can you check whether our certificate scripts and cert-manager config will break with the new shorter TLS certificate validity periods? Don't edit anything yet.”
What it does not do
No network calls; it checks the settings written in your repo, not the certificate a server is serving.
FAQ
What is a Claude Code skill?
A folder with a SKILL.md and scripts that Claude Code loads when your request matches it. You ask in plain words and Claude runs the scanner the skill carries.
How is this different from asking Claude without the skill?
The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of answering from memory.
Does it send my code anywhere?
No network calls; it checks the settings written in your repo, not the certificate a server is serving.
How do I install it?
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "Can you check whether our certificate scripts and cert-manager config will break with the new shorter TLS certificate validity periods? Don't edit anything yet.". Needs Node 16+.
What do I get when I buy?
The zip. On Whop it is in your library as a download lesson with the zip attached; on Gumroad it is the product file.