Claude Code skills · updated 2026-10-03
SSDF attestation audit skill for Claude Code — GitHub Actions SBOM, pinning
Finds each GitHub Actions line that contradicts your SSDF attestation
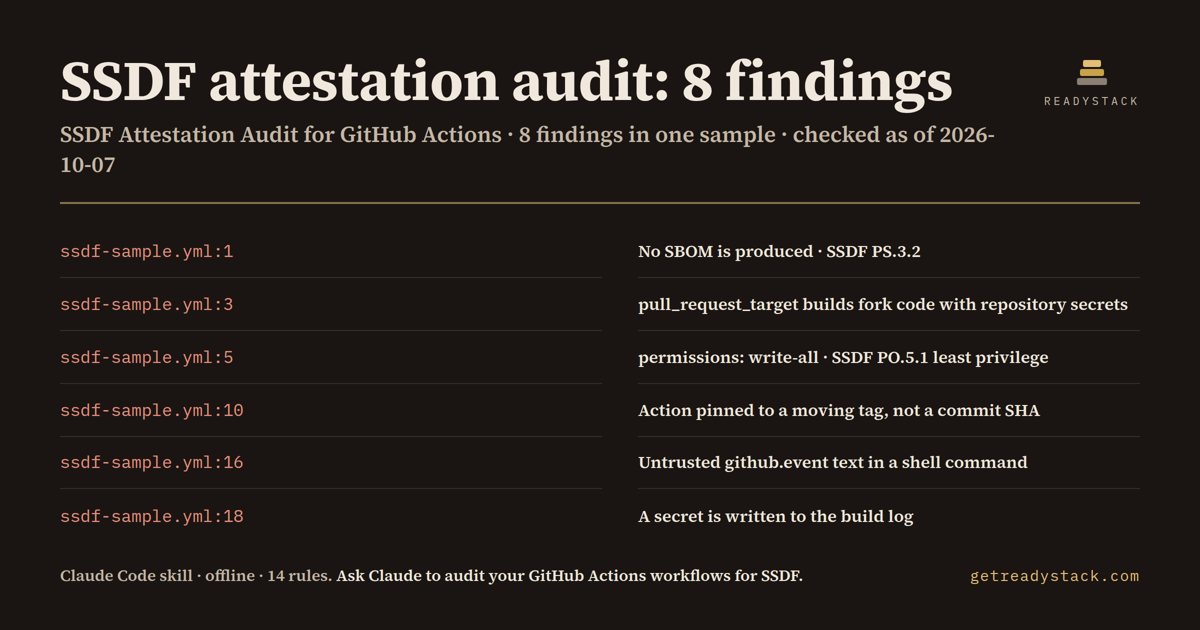
On one 21-line deploy workflow it printed 8 findings (7 errors, 1 warning) from 14 rules, each with file:line, the SSDF practice and the attestation section.
Get it on Whop - $12 onceGet it on Gumroad
Who it's for
For platform and DevSecOps engineers at software vendors who must sign the secure software development attestation for federal customers.
What breaks, and when
A missing SBOM (PS.3.2), no vulnerability check (RV.1.1) or a secret in the build log (PO.5.2) contradicts what the attestation says; the scan dates it against fiscal-year end 2027-09-30.
What it printed on the bundled example
== SSDF Attestation Audit for GitHub Actions — 8 findings (7 errors, 1 warning) in 1 file · 14 rules
  HIGH  ssdf-sample.yml:1  [no_sbom]
        No SBOM is produced - SSDF PS.3.2, attestation section 3 (provenance data). Federal obligations cluster at fiscal-year end 2027-09-30 - 358 days from 2026-10-07.
  HIGH  ssdf-sample.yml:1  [no_vulnerability_check]
        No automated vulnerability check runs - SSDF RV.1.1, attestation section 4. Federal obligations cluster at fiscal-year end 2027-09-30 - 358 days from 2026-10-07.
  HIGH  ssdf-sample.yml:3  [fork_code_with_secrets]
        pull_request_target builds fork code with repository secrets - SSDF PO.5.1, attestation section 1 (secure build environment).
  HIGH  ssdf-sample.yml:5  [token_write_all]
        permissions: write-all gives the job token more than it needs - SSDF PO.5.1 least privilege, attestation section 1.
What you get
- A scanner Claude runs over every workflow file - not a guess from memory
- 14 rules mapped to SSDF PO.5.1, PO.5.2, PW.4.1, PW.4.4, PS.3.1, PS.3.2, RV.1.1, RV.1.2 and attestation sections 1-4
- For each finding: file:line, what is wrong and the replacement line (SHA pin, env: input, npm ci, @sha256)
- Claude proposes the edits and applies them only after you say yes; exit 1 in CI on any high finding
Install
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "We have to sign the SSDF attestation for a federal customer. Can you check whether our GitHub Actions CI is ready? Don't edit anything yet.". Needs Node 16+.
unzip ssdf-attestation-audit.zip -d ~/.claude/skills/
Ask Claude
“We have to sign the SSDF attestation for a federal customer. Can you check whether our GitHub Actions CI is ready? Don't edit anything yet.”
What it does not do
Reads workflow YAML only; it does not call GitHub, resolve tags to SHAs or fill in the attestation form.
FAQ
What is a Claude Code skill?
A folder with a SKILL.md and scripts that Claude Code loads when your request matches it. You ask in plain words and Claude runs the scanner the skill carries.
How is this different from asking Claude without the skill?
The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of answering from memory.
Does it send my code anywhere?
Reads workflow YAML only; it does not call GitHub, resolve tags to SHAs or fill in the attestation form.
How do I install it?
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "We have to sign the SSDF attestation for a federal customer. Can you check whether our GitHub Actions CI is ready? Don't edit anything yet.". Needs Node 16+.
What do I get when I buy?
The zip. On Whop it is in your library as a download lesson with the zip attached; on Gumroad it is the product file.