Claude Code skills · updated 2026-10-03
Security headers skill for Claude Code — dead headers and broken CSP
18 header findings in one _headers file, each with file:line and the reason
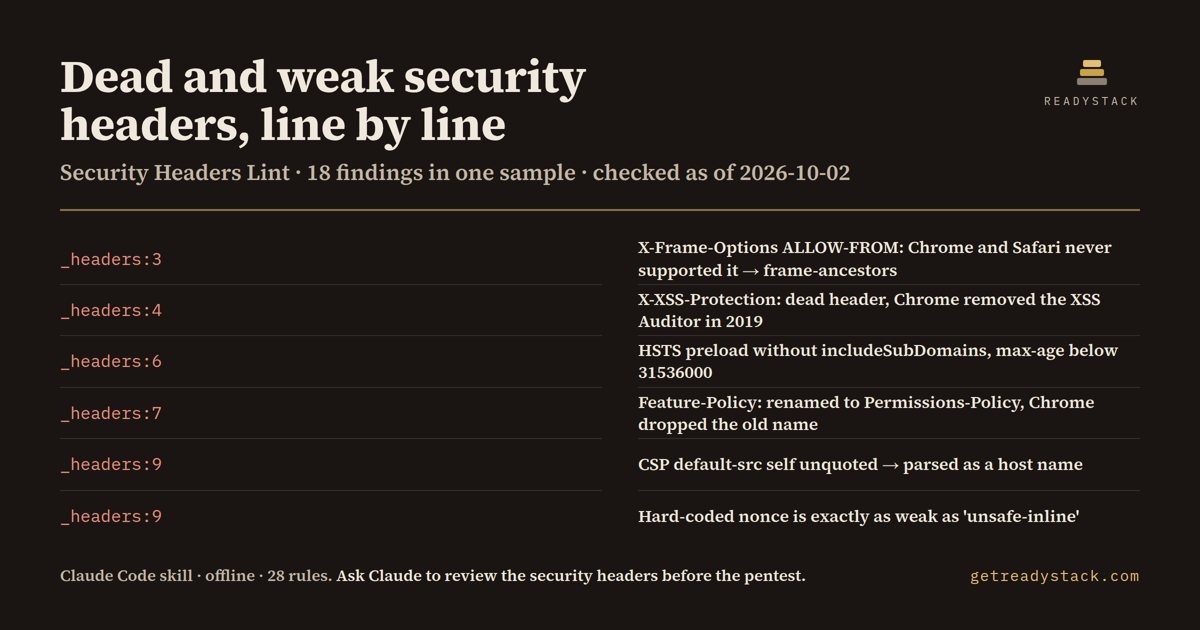
On the bundled sample: 18 findings (11 errors, 4 warnings, 3 info) in 1 file from 28 rules, including ALLOW-FROM, X-XSS-Protection, an unquoted CSP self and a hard-coded nonce.
Get it on Whop - $12 onceGet it on Gumroad
What it printed on the bundled example
== Security Headers Lint — 18 findings (11 errors, 4 warnings, 3 info) in 1 file · 28 rules
  ERROR _headers:3  [shcl_5]
        ALLOW-FROM was only ever implemented by IE and old Firefox. Chrome and Safari have never supported it and treat the whole header as invalid, which can leave the page framable by anyone at all - the opposite of what this line intends. CSP frame-ancestors is the specified replacement and it takes a source list.
        fix: Content-Security-Policy: frame-ancestors 'self' https://partner.example;
  ERROR _headers:4  [shcl_1]
        Dead header. Chrome removed the XSS Auditor in 2019 (Chrome 78), Edge and Safari dropped it too, and Firefox never shipped it, so this line changes nothing in any browser you can install today. The value 1; mode=block was itself exploitable for cross-site info leaks, which is why it was removed. Delete it and let Content-Security-Policy do the work.
        fix: # delete this line - Content-Security-Policy replaces it
  ERROR _headers:5  [shcl_16]
        nosniff is the only value this header defines; anything else leaves MIME sniffing switched on. That matters most where users upload files: a document served with the wrong Content-Type can still be sniffed into script and executed on your origin.
What you get
- SKILL.md, an offline Node scanner (scripts/scan.js) and the 28-rule table
- file:line, severity and why the browser ignores or weakens each header
- Replacement lines, applied only after you agree
- CI: node scripts/scan.js . exits 1 on any error
Install
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "Review the security headers in this repo. Is anything obsolete or not actually enforced? Don't edit anything yet.". Needs Node 16+.
unzip security-headers-review.zip -d ~/.claude/skills/
Ask Claude
“Review the security headers in this repo. Is anything obsolete or not actually enforced? Don't edit anything yet.”
What it does not do
It does not fetch your live site or see headers set by a CDN or app code; no network calls, no edits without your OK.
FAQ
What is a Claude Code skill?
A folder with a SKILL.md and scripts that Claude Code loads when your request matches it. You ask in plain words and Claude runs the scanner the skill carries.
How is this different from asking Claude without the skill?
The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of answering from memory.
Does it send my code anywhere?
It does not fetch your live site or see headers set by a CDN or app code; no network calls, no edits without your OK.
How do I install it?
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "Review the security headers in this repo. Is anything obsolete or not actually enforced? Don't edit anything yet.". Needs Node 16+.
What do I get when I buy?
The zip. On Whop it is in your library as a download lesson with the zip attached; on Gumroad it is the product file.