Claude Code skills · updated 2026-10-03
Rails ERB XSS audit skill for Claude Code — raw/html_safe, script-tag escaping
Finds each raw, html_safe, <%== and <script> value that skips Rails escaping
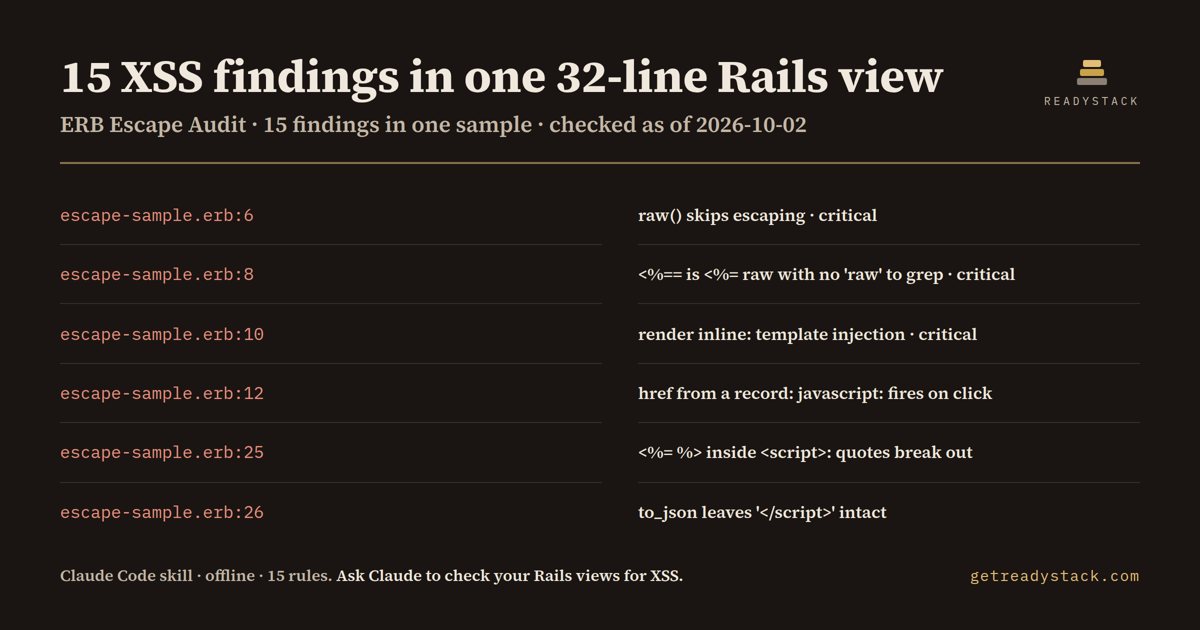
On one 32-line Rails product page it printed 15 findings (11 errors, 4 warnings) from 15 rules, each with file:line, what breaks and the replacement line.
Get it on Whop - $12 onceGet it on Gumroad
What it printed on the bundled example
== ERB Escape Audit — 15 findings (11 errors, 4 warnings) in 1 file · 15 rules
  CRITICAL escape-sample.erb:6  [raw_helper]
        raw() turns the value into HTML and skips escaping - a stored '<script>' in that value runs in every visitor's browser. Drop raw() (<%= value %> escapes by default) or use sanitize(value, tags: %w[b i a]).
  CRITICAL escape-sample.erb:7  [html_safe_call]
        #html_safe marks the string as already-escaped, so ERB prints it verbatim. Remove .html_safe, or build the markup with tag helpers (content_tag/safe_join) so only the literal parts are trusted.
  CRITICAL escape-sample.erb:8  [double_equals_tag]
        <%== is the shorthand for <%= raw - identical unescaped output with no visible 'raw' to grep for. Change it to <%= and escape explicitly where you really need HTML.
  CRITICAL escape-sample.erb:10  [render_inline]
        render inline: compiles the string as an ERB template; user text reaching it is server-side template injection, not just XSS. Render a real template file and pass the value as a local.
What you get
- A scanner Claude runs over every .erb view, partial, layout and mailer template - not a guess from memory
- 15 rules: raw(), .html_safe, <%==, render inline:, <script>/<style> interpolation, to_json, href/on* attributes, link_to params[], unquoted attributes, sanitize() allowlists, CSP unsafe-inline
- For each finding: file:line, what an attacker gets, and the fix (j(), json_escape, a route helper, a data- attribute)
- Claude proposes the edits and applies them only after you say yes; exit 1 in CI on any critical or high finding
Install
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "Can you check our Rails views for XSS? Don't edit anything yet.". Needs Node 16+.
unzip rails-erb-xss-audit.zip -d ~/.claude/skills/
Ask Claude
“Can you check our Rails views for XSS? Don't edit anything yet.”
What it does not do
Reads .erb files only - no Ruby helpers, Haml or Slim; it does not boot Rails or trace data flow, and it is not a replacement for Brakeman.
FAQ
What is a Claude Code skill?
A folder with a SKILL.md and scripts that Claude Code loads when your request matches it. You ask in plain words and Claude runs the scanner the skill carries.
How is this different from asking Claude without the skill?
The skill carries a dated rule table and a scanner that reads every file, so Claude quotes the exact date and line instead of answering from memory.
Does it send my code anywhere?
Reads .erb files only - no Ruby helpers, Haml or Slim; it does not boot Rails or trace data flow, and it is not a replacement for Brakeman.
How do I install it?
Unzip into ~/.claude/skills/ (all projects) or your-repo/.claude/skills/ (one repo), then ask Claude Code: "Can you check our Rails views for XSS? Don't edit anything yet.". Needs Node 16+.
What do I get when I buy?
The zip. On Whop it is in your library as a download lesson with the zip attached; on Gumroad it is the product file.